About
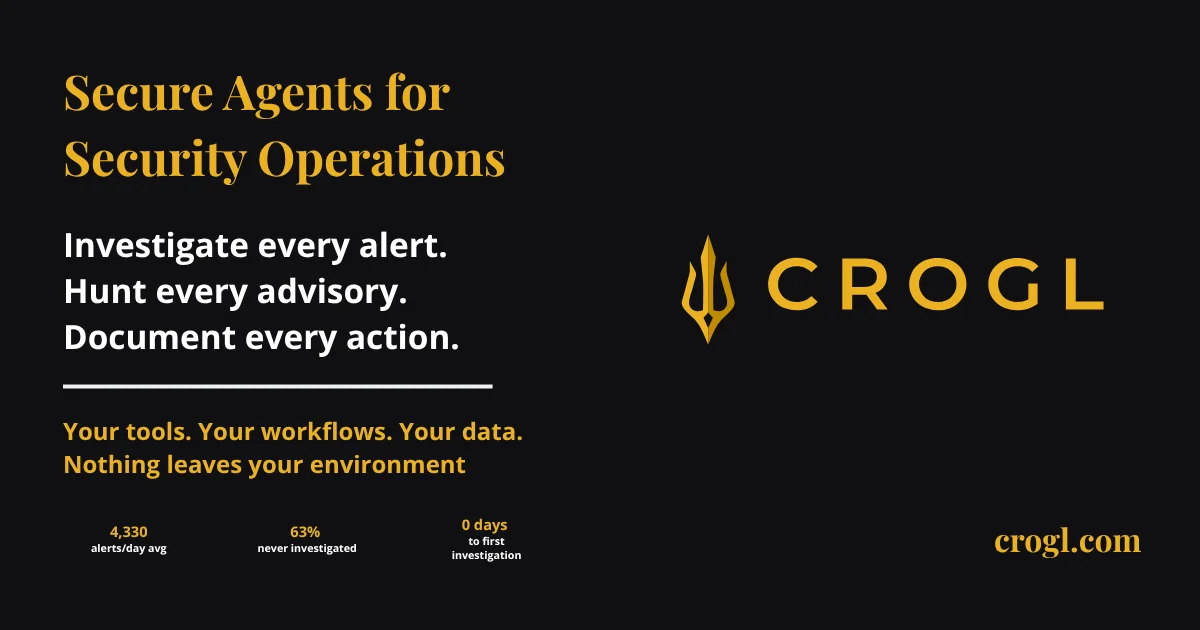
Crogl is an autonomous AI Security Operations Center (SOC) platform built for enterprise and government environments where every alert matters and audit trails are non-negotiable. Rather than routing thousands of daily alerts to overwhelmed analysts, Crogl deploys AI agents that independently gather context, query your tools, cross-reference data across SIEMs, EDRs, cloud logs, and data lakes, and produce complete, auditable investigation reports — all in plain language, with no schema expertise required. The platform ships with production-ready skills for alert triage, threat hunting, endpoint investigation, cloud posture review, phishing analysis, and security advisory processing. A built-in skill builder lets teams define new investigation workflows without hardcoded playbooks — when Crogl encounters a novel threat, it reasons from context rather than waiting for a rule that doesn't exist. Crogl is purpose-built for strict data residency requirements. It deploys on-premises, in a private cloud, or fully air-gapped, ensuring not a single byte of sensitive data leaves the environment. It integrates immediately with existing security stacks — no recoding, no schema normalization required. Crogl is trusted by major US electric utilities, classified US Department of Defense agencies, and Fortune 500 financial institutions. Use cases include SIEM migration without losing detection coverage, reducing mean-time-to-investigate from hours to minutes, and ensuring 100% alert attendance with full audit documentation for compliance teams.
Key Features
- Autonomous Alert Investigation: AI agents investigate every incoming alert end-to-end — gathering context, querying tools, and cross-referencing data — delivering complete, decision-ready findings to analysts instead of raw alert queues.
- Air-Gapped & On-Premise Deployment: Deploy fully on-premises, in a private cloud, or in a classified air-gapped environment. No data ever leaves your infrastructure — this is an architectural guarantee, not a configuration toggle.
- Skills Without Playbooks: Ships with production-ready investigation skills for threat hunting, alert triage, phishing, cloud posture, and more. A built-in skill builder lets teams create new workflows. Crogl reasons from context when encountering novel threats.
- Native Stack Integration: Connects to your existing SIEM, EDR, data lake, and ticketing systems on day one. No schema normalization, no recoding — Crogl queries data in its native format using plain-language analyst requests.
- Full Audit Documentation: Every query, finding, and decision is automatically documented and written back to your ticketing system, providing complete audit trails that satisfy compliance and regulatory requirements.
Use Cases
- A major electric utility uses Crogl to reduce CRISP threat intelligence report analysis from 24+ hours to under 1 hour, protecting critical infrastructure from missed advisories.
- A classified U.S. Department of Defense agency deploys Crogl in an air-gapped environment to ensure 1,000+ daily alerts are fully investigated, with zero data leaving the environment.
- A Fortune 500 financial institution uses Crogl to perform cross-data-lake investigations in minutes instead of ~1 hour, eliminating the need for analysts to memorize every schema and query language.
- SOC teams use Crogl during SIEM migrations to maintain continuous detection coverage without rebuilding playbooks or remapping data schemas to the new platform.
- Enterprise security teams leverage Crogl's autonomous documentation to automatically generate complete audit trails for every investigation, simplifying compliance reporting and regulatory audits.
Pros
- Zero Data Egress: Designed from the ground up for high-security environments — on-premise, private cloud, and air-gapped deployments mean sensitive security data never leaves your organization.
- Immediate Stack Compatibility: Integrates with existing SIEMs, EDRs, data lakes, and ticketing systems on day one without requiring schema rewrites or playbook rebuilding, reducing deployment friction significantly.
- 100% Alert Attendance: Autonomous agents ensure every alert is investigated, eliminating the backlog of uninvestigated alerts that plagues traditional SOC teams and reducing risk of missed threats.
- Compliance-Ready Audit Trails: Every investigation action is fully documented automatically, giving compliance teams the detailed records they need without additional analyst effort.
Cons
- Enterprise-Only Focus: Crogl is purpose-built for large enterprise and government SOCs. Smaller security teams or startups may find the platform more than they need and potentially cost-prohibitive.
- No Public Pricing: Pricing is not publicly listed, requiring direct engagement with the sales team, which can slow down evaluation for organizations comparing multiple vendors.
- Requires Existing Security Stack: Crogl works alongside your existing SIEM, EDR, and data infrastructure. Organizations without a mature security stack in place will need foundational tooling before fully leveraging the platform.
Frequently Asked Questions
Does Crogl require data to be sent to external servers?
No. Crogl is architected so that no data ever leaves your environment. It can be deployed fully on-premises, in a private cloud, or in a completely air-gapped classified environment. Data residency is an architectural guarantee, not a configuration option.
Does Crogl replace security analysts?
No. Crogl is designed to elevate analysts, not replace them. It handles the investigative groundwork — querying tools, gathering context, cross-referencing data — so analysts spend their time making informed decisions rather than running manual queries.
What security tools does Crogl integrate with?
Crogl integrates with your existing SIEM, EDR, data lakes, cloud logs, and ticketing systems on day one. It queries data in its native format, requiring no schema normalization or recoding.
Does Crogl require predefined playbooks to operate?
No. Crogl ships with production-ready investigation skills and a skill builder for custom workflows. Unlike rule-based automation, when Crogl encounters a novel or unexpected threat, it reasons from context rather than stopping due to a missing rule.
Can Crogl help with SIEM migrations?
Yes. Because Crogl abstracts investigation logic away from the SIEM layer, teams can migrate to a new SIEM without rebuilding playbooks, remapping schemas, or losing detection use cases.