About
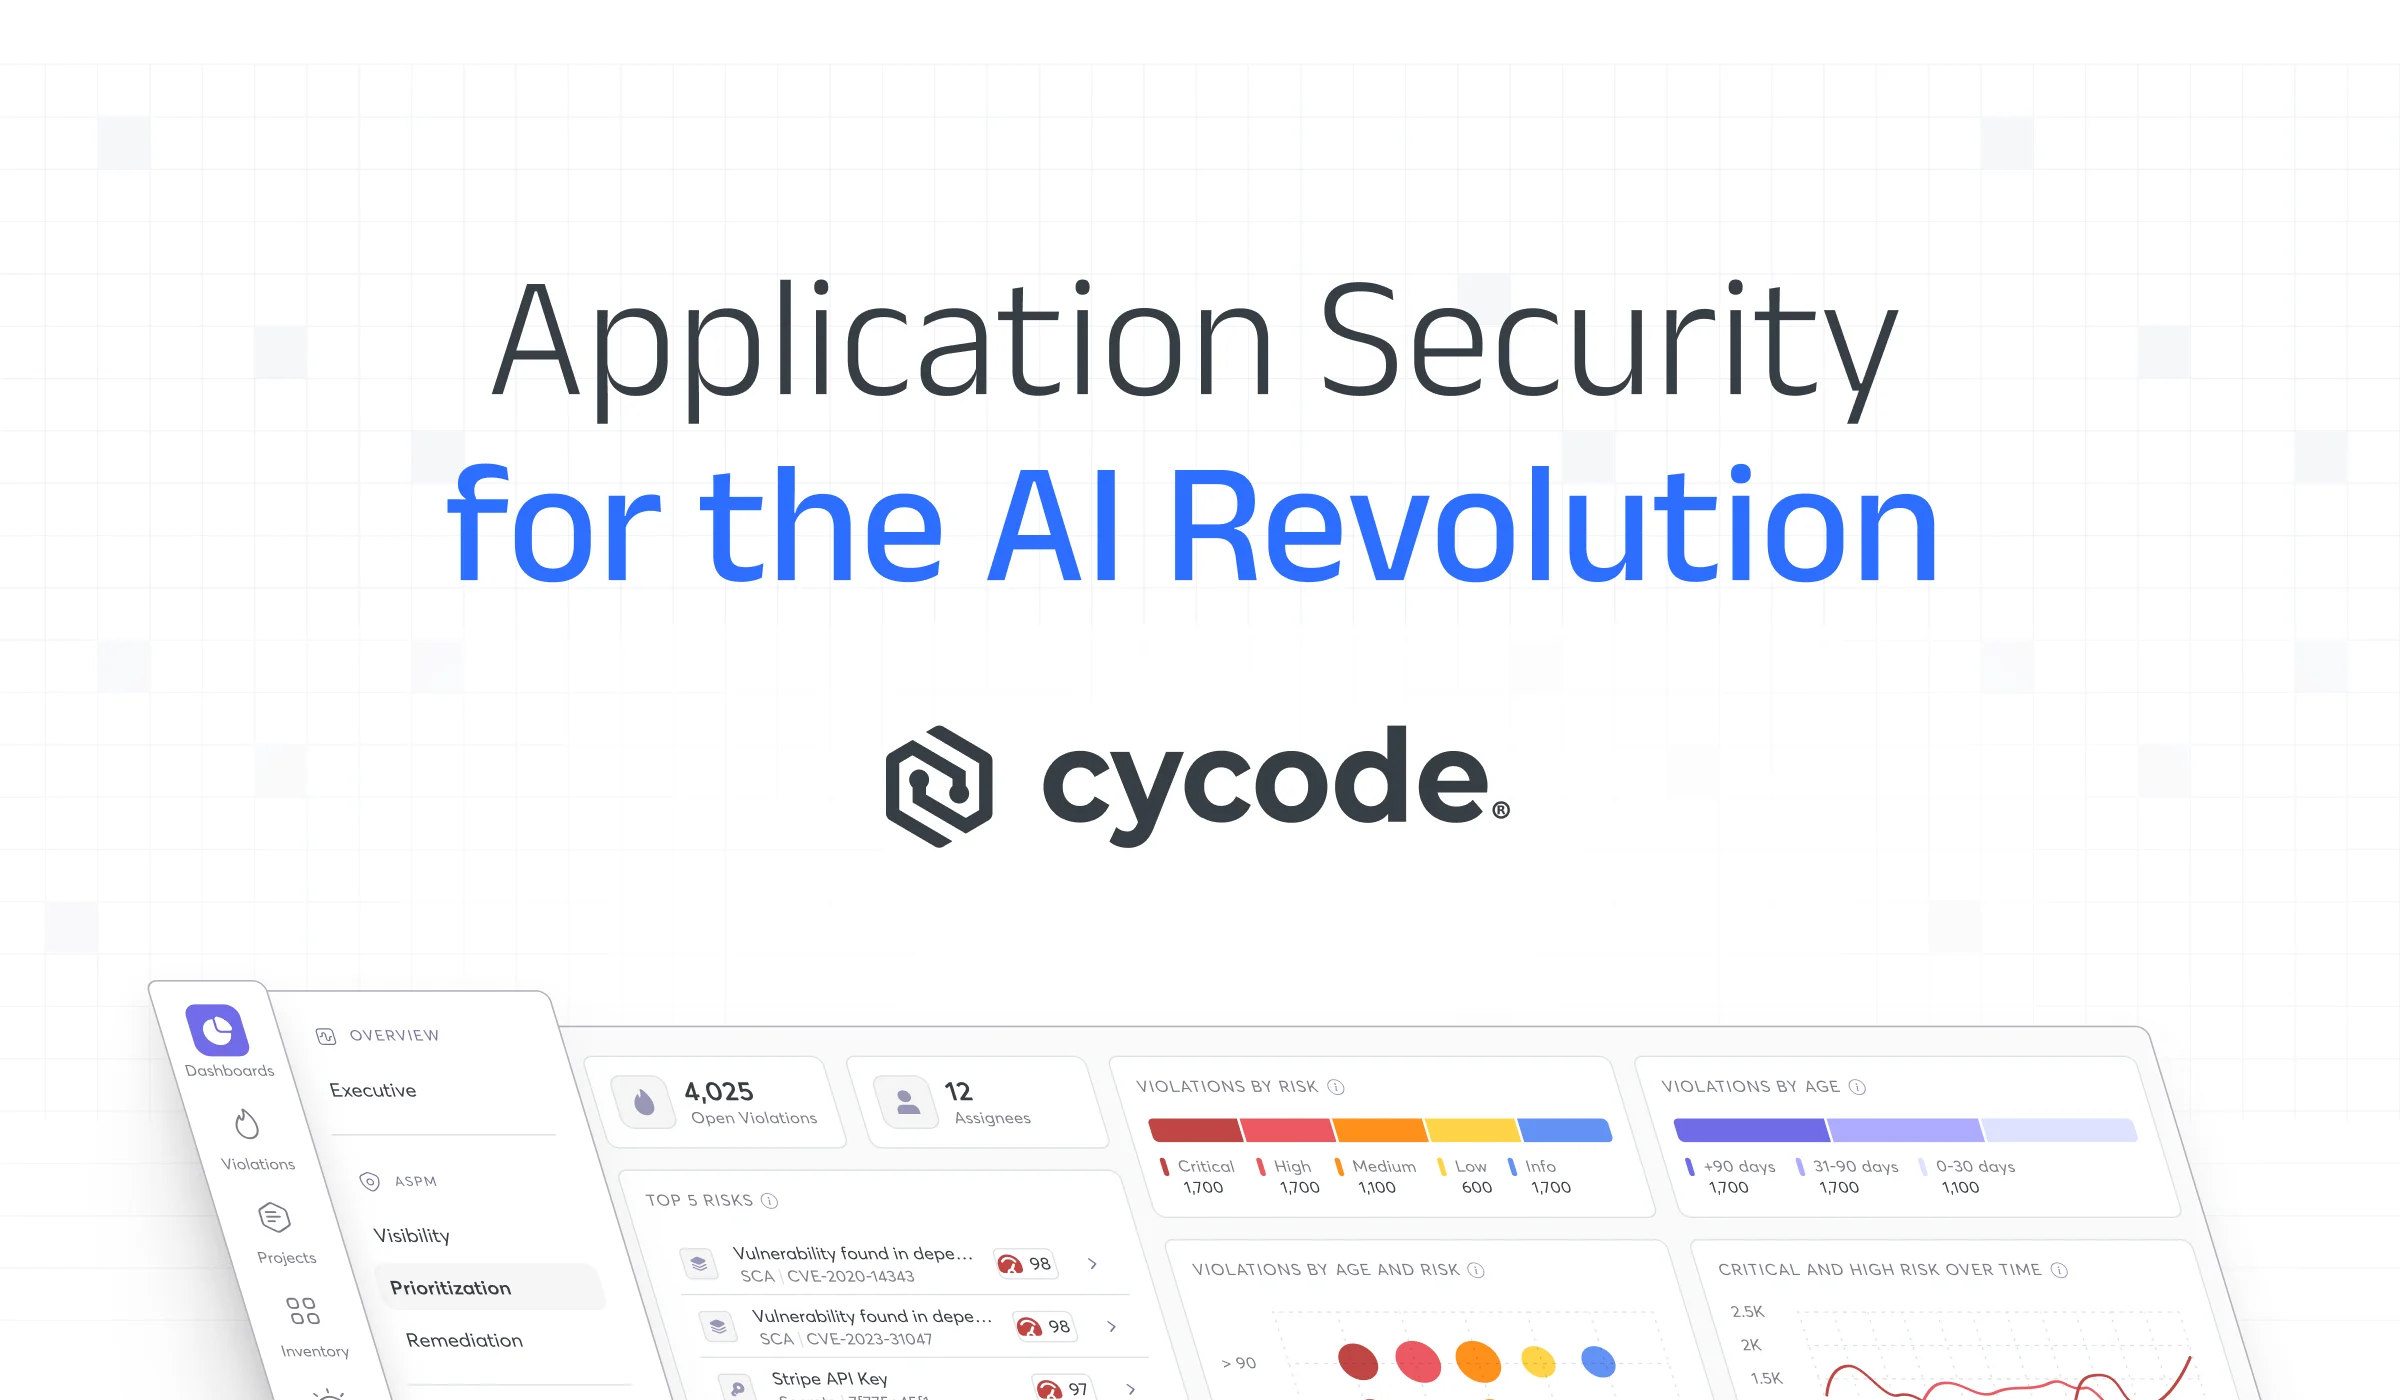
Cycode is a comprehensive Agentic Development Security Platform (ADSP) designed to bring together security teams, developers, and AI agents under one unified platform. Built around the vision of a Self-Protecting ADLC™, Cycode delivers end-to-end application security from the earliest stages of development all the way to runtime. The platform leverages Cycode AI Maestro — its AI orchestration brain — to provide intelligent security engineering at scale through agentic capabilities. Key capabilities include SAST & AI SAST, Software Composition Analysis (SCA), Secrets Detection, Container Security, Infrastructure as Code (IaC) Security, and CI/CD pipeline protection. Cycode also offers Supply Chain Risk Management (SSCS), SBOM & AI-BOM generation, and Change Impact Analysis to provide full visibility into modern software supply chains. For AI governance, Cycode provides AI Visibility, AI Guardrails, AI Risk Detection, and an AI Bill of Materials (AI-BOM) to help organizations securely govern the AI layer within their development lifecycle. Risk posture features include a Risk Intelligence Inventory, 100+ connectors, Custom Dashboards, and Compliance Reporting to give CISOs and security leaders actionable insights. Cycode is trusted by leading enterprises worldwide and has been ranked #1 in SSCS in the Gartner® 2025 Critical Capabilities report and entered the Gartner® AST Magic Quadrant™ 2025. It is ideal for large development organizations, security engineers, and CISOs looking to scale application security with AI-driven automation.
Key Features
- AI Maestro Orchestration: Cycode's AI brain that coordinates agentic security engineering at scale, including AI Fix & Remediation Agents, AI Exploitability Agents, and Change Impact Analysis Agents.
- Comprehensive AST Scanning: Includes SAST, AI SAST, SCA, Secrets Detection, Container Security, and IaC Security for deep, deterministic scanning augmented by AI reasoning.
- Supply Chain & CI/CD Security: Protects modern software supply chains with CI/CD pipeline security, SBOM & AI-BOM generation, code leakage detection, and runtime protection.
- AI Governance & Guardrails: Provides AI Visibility, AI Governance, AI Guardrails, and AI-BOM to secure and govern the AI layer within your application development lifecycle.
- Risk Intelligence & Compliance: Offers a Risk Intelligence Inventory, 100+ connectors, custom dashboards, reporting & analytics, and compliance tracking for full CISO-level visibility.
Use Cases
- Enterprise security teams seeking to unify AST, ASPM, and supply chain security into a single AI-powered platform.
- DevSecOps teams automating vulnerability detection and remediation across CI/CD pipelines to shift security left.
- CISOs and security leaders requiring full code-to-runtime risk visibility, compliance reporting, and executive-level dashboards.
- Organizations governing AI-generated code and agentic development workflows with AI guardrails and AI-BOM tracking.
- Software development organizations managing third-party supply chain risk through SBOM generation, SCA scanning, and CI/CD integrity monitoring.
Pros
- Unified Security Platform: Converges AST, ASPM, and SSCS into a single platform, reducing tool sprawl and giving teams a holistic view of application security risk.
- AI-Native Automation: Agentic AI capabilities automate detection, prioritization, and remediation, significantly reducing manual security effort and accelerating fix cycles.
- Gartner-Recognized Leader: Ranked #1 in SSCS in Gartner® 2025 Critical Capabilities and featured in the Gartner® AST Magic Quadrant™, demonstrating market-leading credibility.
- Broad Integration Support: 100+ connectors enable seamless integration with existing development and security toolchains, minimizing friction during adoption.
Cons
- Enterprise-Focused Complexity: The breadth of features and enterprise orientation may be overwhelming or over-engineered for smaller teams or startups with simpler security needs.
- Pricing Transparency: Pricing is not publicly listed, requiring a demo or sales engagement to evaluate costs, which can slow procurement decisions.
- Learning Curve: With a wide range of modules spanning AST, SSCS, ASPM, and AI governance, teams may require significant onboarding time to fully leverage the platform.
Frequently Asked Questions
What is Cycode's Agentic Development Security Platform?
Cycode's ADSP is an AI-native security platform that secures the entire application development lifecycle (ADLC) from prompt to runtime. It combines AST, ASPM, and SSCS capabilities with agentic AI to detect, prioritize, and remediate software risks automatically.
What security tools does Cycode include?
Cycode includes SAST, AI SAST, SCA, Secrets Detection, Container Security, IaC Security, CI/CD Security, Supply Chain Risk Management, SBOM & AI-BOM generation, and risk posture management — all within a single unified platform.
How does Cycode use AI in its platform?
Cycode uses AI Maestro as its central orchestration engine, powering AI Exploitability Agents, AI Fix & Remediation Agents, Change Impact Analysis Agents, and a Context Intelligence Graph to deliver intelligent, automated security at scale.
Is Cycode suitable for enterprises?
Yes. Cycode is purpose-built for enterprise development organizations. It supports 100+ integrations, provides compliance reporting, offers CISO-level dashboards, and has been recognized by Gartner as a market leader in application security.
Does Cycode support AI governance?
Yes. Cycode includes a dedicated AI governance suite with AI Visibility, AI Guardrails, AI Risk Detection, and AI-BOM to help organizations manage and secure the AI components within their software development pipelines.